
DPIAs are mandatory (GDPR, Article 35) exercises if you process personal data in a way that may present a high risk to people. They also add value to business:
- Reduce wasteful data processing and storage,
- Minimises risks of data breaches and damage to your reputation,
- Prevent unlawful or rogue processing,
- Demonstrates conformity with privacy by design and by default principles,
- Helps organisations avoid fines, investigations and sanctions,
- Garners trust in your brand from regulators, supply-chain partners, potential investors and of course your end-customers.
FRIAs are mandatory exercises (AI Act, Article 27) for developers, importers, resellers and deployers of High Risk AI, to complete before being sold in the EU. The FRIA:
- Is a market-entry artefact for businesses that deal in AI solutions
- Provides evidence that necessary due-diligence has been applied by organisations,
- Complements completed DPIA exercises to establish public and institutional trust in your AI innovations.
- Includes a description of AI processes; time and frequency of use; people or groups affected; risks, harms and mitigative measures; human oversights and steps to take when risks arise.
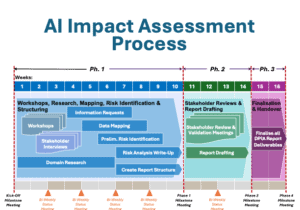
An AI Impact Assessment (AIIA) is a structured process for evaluating positive and negative consequences of AI systems before deployment.
- Extends DPIA risk-based exercises to include bias, discrimination and transparency to ensure AI is ethical, legal and responsible.
- Helps organizations meet regulatory requirements of the EU AI Act by acting to mitigate identified risks.
- Builds trust in responsible AI by undertaking risk assessments at each stage in the lifecycle.
- Helps organisations proactively manage AI risk to reduce prospect of legal challenge, fines and reputational damage.
AICAs are mandatory (AI Act, Article 43) exercises that need to be successfully undertaken before a "CE" mark is assigned to an AI solution before launch in the EU Market.
- Providers of High-Risk AI must undertake these assessments which include a declaration of conformity confirming compliance before a CE marking can be affixed.
- This assessment evaluates systems against risk management, data governance, transparency and human oversight criteria.
- Also a required exercise for individual AI-based technology components, developed by supply-chain partners, that will incorporated into larger AI solutions.
If your organisation requires an Impact Assessment, whether its a DPIA, FRIA, AICA or AIIA please talk to us to discuss what's required to complete these exercises.